Smart Contract Audits & Penetration Testing for EVM, Solana and Beyond
Our auditors combine leading AI with in-house deterministic analysis tools to speed up every review, every pen test for your project. Our London-based team covering EVM, Solana and the other major chains.
Enterprise level security at a fraction of traditional costs
Version-linked. Publicly verifiable. No marketing edits.
An audit is a snapshot, and your code does not stop
Issues with Audits
A traditional audit certifies a specific commit on a specific day. Then you ship. Dependencies move, parameters change, a module lands, and the conclusion in the report quietly stops describing what is deployed. Nobody did anything wrong. The audit simply decayed.
Audit Solution
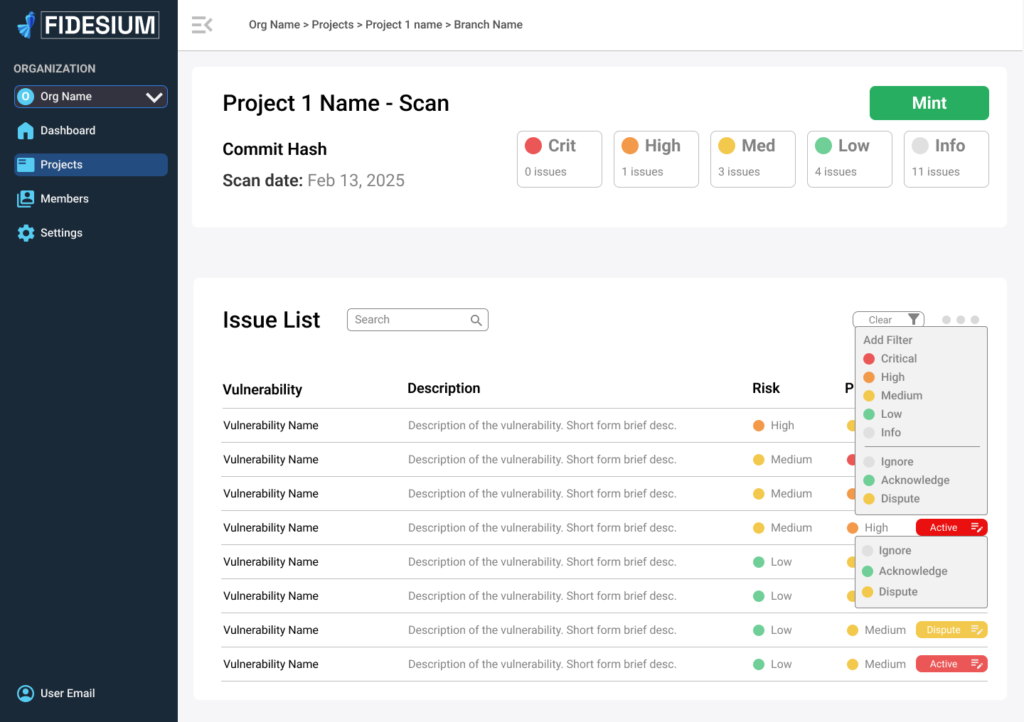
That is the gap Fidesium was built to close. Every audit we deliver is minted as an on-chain record of what was reviewed, at which commit, on which date, so it is verifiable without asking us. And our own static analysis keeps running, on every commit, pull request and deployment, against the logic the audit relied on. It is deterministic, so the same code returns the same result every time, which is the property that makes an audit record worth minting.
Audit Proof
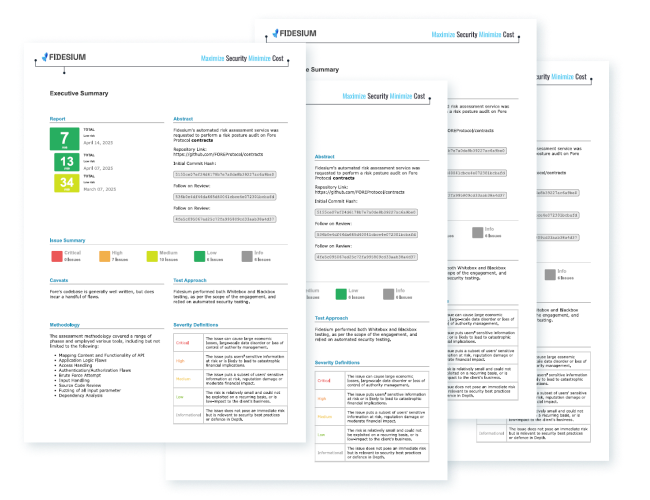
The work is public. Read the 23 reports, covering 16 protocols, and see the findings, the severities and the remediation before you speak to anyone here. Or request a quote and tell us the repository, the commit and the deadline.
Version-linked. Publicly verifiable. No marketing edits.
Trusted by protocols and founders
Our clients love the speed, accuracy and cost of Fidesium automated audits.
“Fidesium was instrumental to improving our dev cycle times while keeping our customers and the protocol secure.”
“Fidesium's real time scans of our contract and the risks present allowed us to deploy more secure code faster.”
“This is a super impressive summary though, really insightful... gonna get my head down and tick off these crits!”
“The audit produced very actionable results and helped us improve our code base.”
The Traditional Audit Model is Broken
Expensive Re-Audits
$50K-$150K per audit
Pay full price for minor updates
Unpredictable security budget
Point-in-Time Coverage
Faster development for immutable contracts
Audits expire when code changes
No protection between audits
Weeks of blocked shipping
Trust Without Proof
Static PDF reports
No ongoing verification
Difficult for exchanges/investors to validate
You shouldn’t have to choose between security and speed-to-market. Security should not hinder your growth, drain your pocket and slow your project.
How is Fidesium different from traditional audits?
Traditional audits review your code at a single point in time. Once code changes, the assumptions behind that audit may no longer hold.
Fidesium extends the value of audits over time. It supports both manual and automated audits by re-running audit-grade checks when meaningful code changes occur, helping teams understand what remains covered, what needs review, and why.
This turns audits from static reports into version-aware security evidence.
How do your manual audits compare to firms other top?
The difference? We offer the same quality of security at 60-70% lower cost because our business model includes an ever improving tool to help our auditors and ongoing automated coverage that reduces the need for expensive re-audits. We also offer a machine readable verifiable record of your audit history as an NFT
Do I still need a manual audit if I use your automated tool?
Yes.
Automated tools catch ~89% of common vulnerabilities, but complex business logic, novel attack vectors, and context-specific issues require human expertise. Our hybrid model gives you both.
What happens if you find a vulnerability after deployment?
If our continuous scanning detects a new vulnerability post-deployment, we alert you immediately with severity classification and remediation guidance. Critical issues get direct contact with an auditor.
How long does a manual audit take?
Most audits complete in 1-3 weeks depending on complexity. We provide a detailed timeline during scoping.
What if I need re-auditing after making changes?
Traditional manual audits often force teams into costly re-audits after even minor changes. Fidesium reduces this overhead by covering incremental updates through continuous automated rescanning, limiting manual re-reviews to meaningful architectural changes and cutting re-audit costs by up to 60%.
What's included in security consulting?
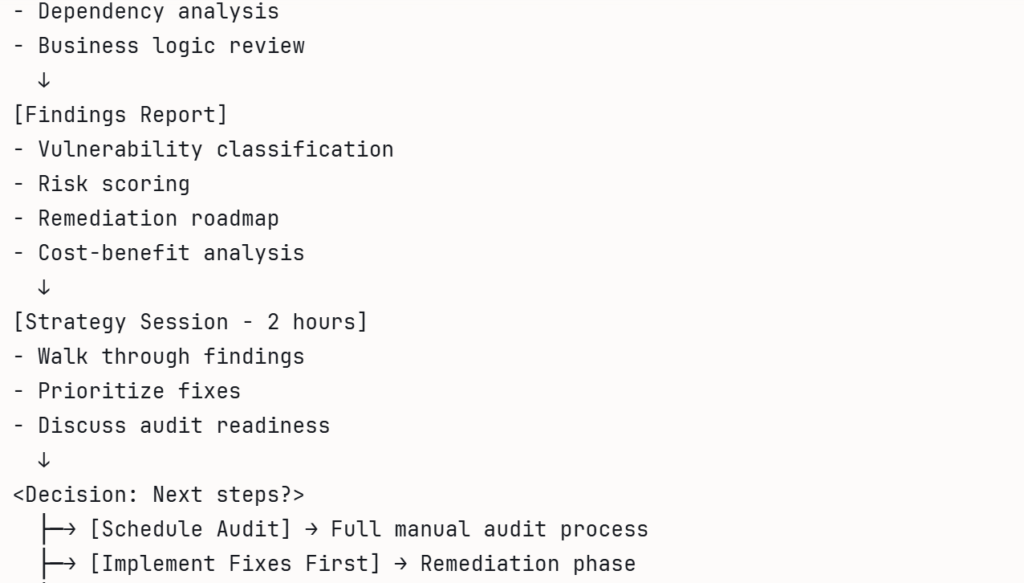
Solutions vary on a case to case basis, but in general;
Available as standalone service or bundled with audits.
How does your scanner differ from open source static analysis tools?
Fidesium’s scanner, relies on many open source frameworks and extends them significantly.
1000+ custom detectors for critical edge cases.
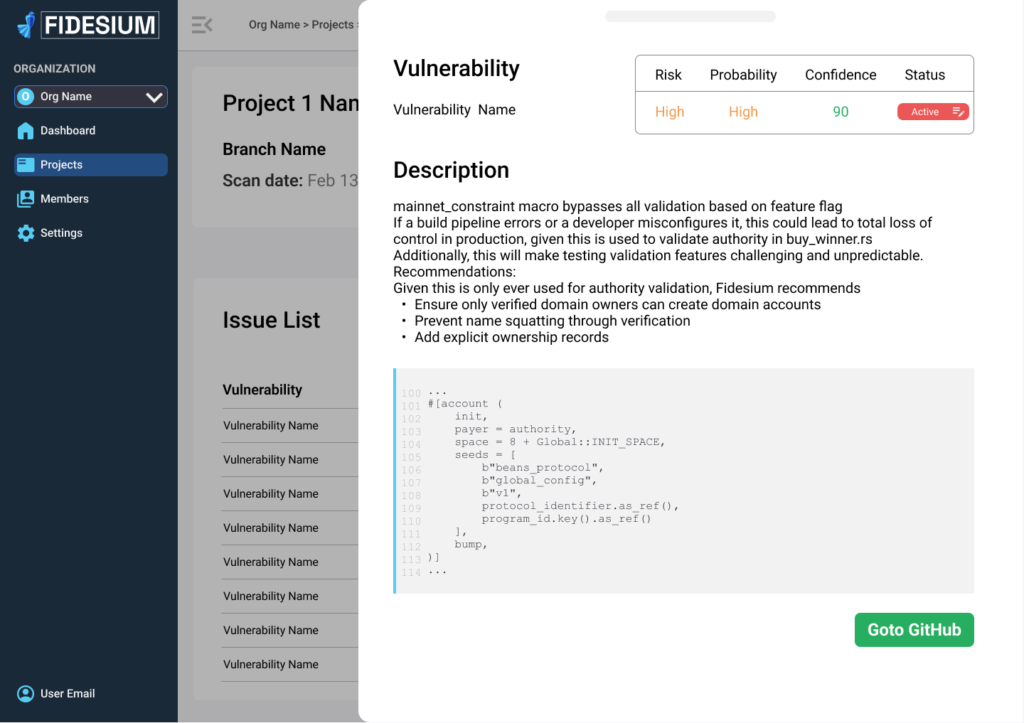
Fidesium’s scanner is also change-aware, and fits into your development flow. Making it easier and faster to scan code as it develops. SARIF generation for compliance and interoperability.
CI/CD integration, reduces friction, deployment gate to stop vulnerable code from hitting production.